When you open the SAP Fortinet NSE 4 - FortiOS 7.2 material on TestsDumps, you are not just getting 184 questions. Each set is shaped into a study strategy by trainers who know how candidates learn, which is what makes C-HRHFC-2311 preparation at TestsDumps feel guided rather than random.
SAP C-HRHFC-2311 Exam Syllabus Topics:
| Section | Objectives |
|---|---|
| Topic 1: Firewall Policies and NAT | - Firewall Configuration
|
| Topic 2: Monitoring and Troubleshooting | - Logging and Reporting
|
| Topic 3: High Availability and SD-WAN | - High Availability
|
| Topic 4: Authentication and Access Control | - VPN
|
| Topic 5: Security Profiles | - Threat Protection
|
| Topic 6: System and Network Settings | - Initial Configuration
|
Frequently Asked Questions About C-HRHFC-2311 Preparation
No formal prerequisite. Fortinet recommends completing the FortiGate Administrator and FortiGate Infrastructure training courses and having hands-on experience with FortiGate devices.
The C-HRHFC-2311 exam contains 60 questions and lasts 105 minutes minutes, so pacing matters as much as knowledge. Practicing under a real timer on TestsDumps helps you learn how long to spend on each item.
The SAP Fortinet NSE 4 - FortiOS 7.2 material is written by a group of IT experts and certified trainers. Beyond assembling verified questions, they organize the bank into a study strategy for candidates, so you always know which section to tackle next instead of paging through questions at random.
The online engine recreates the atmosphere of the formal test, so the real C-HRHFC-2311 exam feels familiar rather than intimidating. It runs on Windows, Mac, Android, and iOS, places no limit on the number of installations, and lets you review at any time and from any location, which fits naturally around an IT worker's schedule.
The passing score of C-HRHFC-2311 is Pass/Fail, and the official exam fee is $400 USD. Knowing both numbers early helps you set a concrete target before you book the test.
This package includes 184 practice questions for the C-HRHFC-2311 exam. Every answer has been verified by our IT experts and certified trainers before release.
- Authentication and Access Control ()
- Monitoring and Troubleshooting ()
- High Availability and SD-WAN ()
Study the sections in the order that matches your weakest areas first.
SAP Fortinet NSE 4 - FortiOS 7.2 Sample Questions:
Refer to the exhibit.
The exhibit shows a diagram of a FortiGate device connected to the network, the firewall policy and VIP configuration on the FortiGate device, and the routing table on the ISP router.
When the administrator tries to access the web server public address (203.0.113.2) from the internet, the connection times out. At the same time, the administrator runs a sniffer on FortiGate to capture incoming web traffic to the server and does not see any output.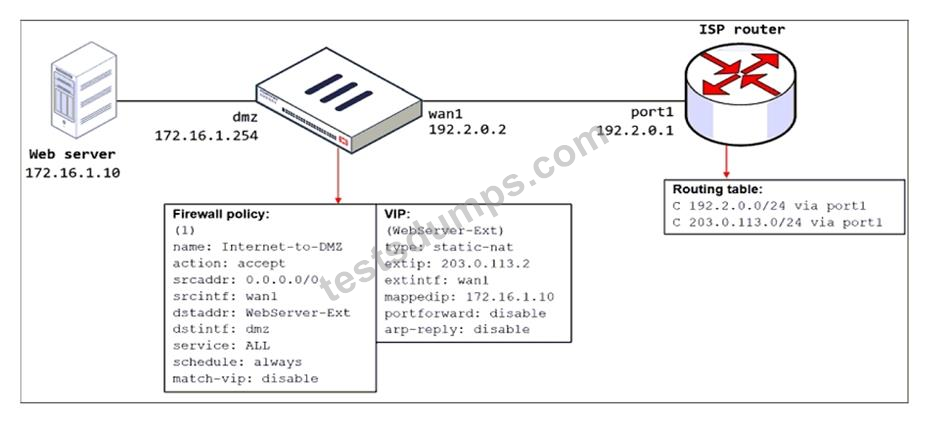
Based on the information shown in the exhibit, what configuration change must the administrator make to fix the connectivity issue?
- A. Enable port forwarding on the server to map the external service port to the internal service port.
- B. In the firewall policy configuration, enable match-vip.
- C. In the VIP configuration, enable arp-reply.
- D. Configure a loopback interface with address 203.0.113.2/32.
Correct Answer: C 🗳️
Explanation: Only visible for TestsDumps members. You can sign-up / login (it's free).
If Internet Service is already selected as Destination in a firewall policy, which other configuration object can be selected for the Destination field of a firewall policy?
- A. IP address
- B. No other object can be added
- C. FQDN address
- D. User or User Group
Correct Answer: B 🗳️
Explanation: Only visible for TestsDumps members. You can sign-up / login (it's free).
A network administrator is troubleshooting an IPsec tunnel between two FortiGate devices. The administrator has determined that phase 1 fails to come up. The administrator has also re-entered the pre-shared key on both FortiGate devices to make sure they match.
Based on the phase 1 configuration and the diagram shown in the exhibit, which two configuration changes will bring phase 1 up? (Choose two.)
- A. On HQ-FortiGate, set IKE mode to Main (ID protection).
- B. On both FortiGate devices, set Dead Peer Detection to On Demand.
- C. On HQ-FortiGate, disable Diffie-Helman group 2.
- D. On Remote-FortiGate, set port2 as Interface.
Correct Answer: A,D 🗳️
Explanation: Only visible for TestsDumps members. You can sign-up / login (it's free).
In an explicit proxy setup, where is the authentication method and database configured?
- A. Proxy Policy
- B. Authentication Rule
- C. Authentication scheme
- D. Firewall Policy
Correct Answer: C 🗳️
Refer to the exhibits.
Exhibit A shows a topology for a FortiGate HA cluster that performs proxy-based inspection on traffic. Exhibit B shows the HA configuration and the partial output of the get system ha status command.

Based on the exhibits, which two statements about the traffic passing through the cluster are true? (Choose two.)
- A. The traffic sourced from the client and destined to the server is sent to FGT-1.
- B. For non-load balanced connections, packets forwarded by the cluster to the server contain the virtual MAC address of port2 as source.
- C. The cluster can load balance ICMP connections to the secondary.
- D. For load balanced connections, the primary encapsulates TCP SYN packets before forwarding them to the secondary.
Correct Answer: B,D 🗳️
Explanation: Only visible for TestsDumps members. You can sign-up / login (it's free).
Viewing page 1 out of 37 pages.
Viewing questions 1-5 out of 184 questions.


 Bing

 Heather
 Susan

 Gilbert
 Matt
 Marvin
 Les
 Muriel

 Michell
 Eudora
 Frederic
 Gene
 Hyman
 Eudora
 Blanche
 Marlon
 Norman
 Noel
 Hunter
 Myron